Operational resilience is being redefined as an audit task rather than a legal filing, forcing fintech leadership to address technical debt before the 2027 enforcement deadline. The current atmosphere across London and Washington mirrors the final months before a systemic shift in financial
Achieving certification requires organizations to integrate cloud-specific requirements directly into their existing Statement of Applicability. The transition to cloud infrastructure has fundamentally altered the perimeter of corporate networks, moving from physical barriers to software-defined
During the height of the disruption, archive and raw-content download failure rates climbed to a staggering fifty percent, effectively paralyzing development workflows globally. This catastrophic event originated from what appeared to be a routine network update, yet it quickly spiraled into a
Financial demands from the Medusa group have scaled alongside their technical sophistication, with some ransom requests reaching fifteen million dollars for a single organization. This escalation highlights a broader trend where cyber-syndicates have moved beyond simple opportunistic attacks to
Most organizations lack visibility into where public-key cryptography is embedded within their infrastructure, making a comprehensive cryptographic inventory the essential first step toward quantum resilience. This foundational awareness is becoming increasingly urgent as the development of quantum
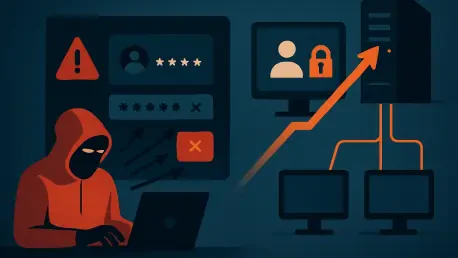
Threat actors often employ a multi-stage process involving initial password spraying followed by privilege escalation to establish persistence within a target organization. This methodology has proven remarkably effective as digital environments expand, often leaving identity as the only remaining