Implementing strict secret management protocols and immediate key revocation is now essential for organizations to defend against high-volume automated reconnaissance campaigns. As the integration of large language models into corporate workflows continues to accelerate, API keys have emerged as a
For over twenty years, software engineers have performed a digital penance, spending countless hours meticulously repairing the brittle scripts that sustain the modern internet; this labor-intensive cycle of Quality Assurance (QA) reached a critical saturation point as software complexity outpaced
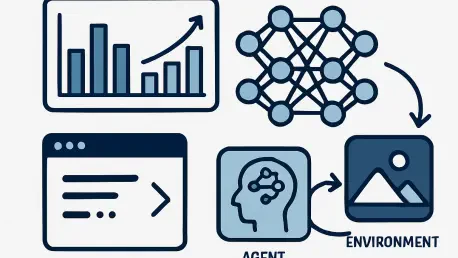
Evaluating a policy with the evaluate_policy helper provides a streamlined way to calculate the mean reward across multiple episodes without manual loop construction. This capability sits at the heart of Stable-Baselines3, a library that has fundamentally transformed how researchers and developers
System maintenance tools like FluentCleaner provide a dedicated terminal tab for advanced users who prefer a command-line interface for routine optimization tasks. This specific functionality represents a significant shift in the 2026 software landscape, where the democratization of development
Despite an urgent need to mitigate trade-related risks, many businesses remain paralyzed by the technical challenges of decoupling from their current providers. This pervasive state of inertia occurs at a time when digital sovereignty has transitioned from a theoretical preference to a critical
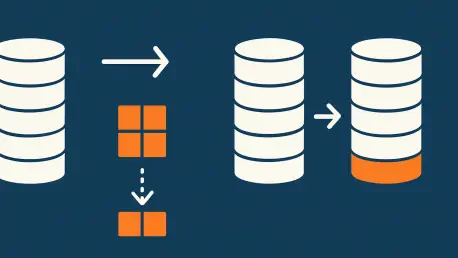
In the high-stakes environment of enterprise data management, the choice between processing every record or only those that have changed can determine whether a business intelligence platform thrives or stalls under its own weight. This decision rests at the heart of every data warehouse project,
Small businesses face a relentless barrage of cyberattacks that often outpace their limited administrative capacities, creating a desperate need for consolidated security frameworks. The shift from an integrated password tool to a standalone browser extension requires a calculated migration
Organizations utilizing Langflow for AI application development face significant risks as unauthenticated attackers can now exploit network vulnerabilities to gain full system control. This alarming reality stems from a series of high-severity vulnerabilities discovered within the open-source
Autonomous discovery processes allow engineering teams to identify accessibility issues in obscure areas of an application that are typically overlooked by humans. This specific capability is becoming the cornerstone of a major shift in how quality assurance is handled in the modern development
Cybercriminals often use high-severity flaws like this one to install coin-mining software or establish remote-control backdoors within corporate software environments. This reality is currently being felt across the global development community as a critical vulnerability in GitLab, the widely


