Simply rotating individual secrets is insufficient for remediation when the underlying write access to the repository remains in the hands of an attacker. GhostAction has established itself as a cornerstone of modern supply chain risks, specifically targeting GitHub Actions in a way that turns
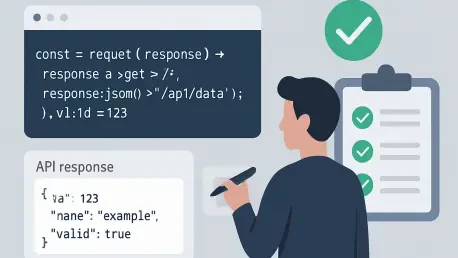
Basic assertions serve as a primary layer of verification to confirm endpoint stability and data presence before performing deeper structural checks. In the current landscape of 2026, where microservices dominate the software architecture, the reliability of communication between these services
Using a cross-project five-fold GroupKFold protocol prevents data leakage, ensuring that predictive models remain accurate when applied to entirely new software projects. This sophisticated methodological approach sits at the heart of QualiGuard, a system designed to address the growing friction
Mid-market companies and startups are increasingly turning to value insurgents that offer consolidated security stacks designed specifically to reduce noise for resource-constrained engineering teams. This shift marks a definitive departure from the fragmented best-of-breed era that characterized
A major pitfall in DevSecOps implementation occurs when platforms are used as procurement exercises rather than catalysts for necessary cultural shifts between teams. The software development environment in 2026 is defined by a tense balance between the demand for rapid delivery and an increasingly
When a senior software engineer looks at a block of AI-generated code today, they are no longer asking if the logic sounds plausible but rather if the surrounding system has already verified its execution within a secure sandbox. This shift in perspective represents the definitive end of the