Every build failure triggered by an automated security gate forces developers to re-execute every previous stage of the pipeline, including unit tests and linting. This circular workflow might seem like a minor inconvenience, but at scale, it represents a massive drain on organizational resources.
Automated build pipelines for medical device manufacturers and industrial leaders like Dräger and Bosch were caught in the wide-reaching net of the Trivy-to-LiteLLM attack chain. This sophisticated operation, uncovered by security researchers, exposed the inherent vulnerabilities in the modern
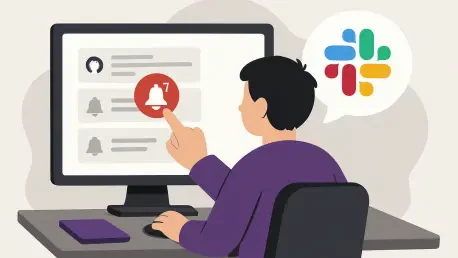
Strategic use of daily summaries and snapshots helps teams digest a day’s worth of repository activity in minutes rather than hours spent monitoring individual notifications. In the current landscape of 2026, software development teams have moved their primary operational focus into Slack,
Continuous integration pipelines specifically designed for radio frequency applications use mathematical validation to ensure that new signals fall within legal and technical parameters. This transition represents a profound departure from the legacy era of static radio hardware, where
Engineering teams managing massive codebases must now weigh the maturity of ESLint’s ten-year plugin ecosystem against the raw throughput of Oxlint, which can process over eleven thousand files per second. This shift represents a fundamental transformation in how JavaScript and TypeScript
Security teams are facing a significant blind spot as malware authors transition from install-time scripts to repository-specific configurations that govern how IDEs interact with code. This shift in methodology is center stage in the ChainDrop campaign, a sophisticated operation that has recently