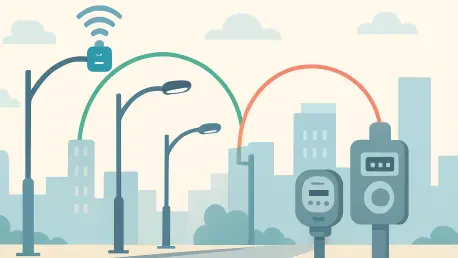
The purchase-first mentality prevalent in local government procurement often results in the onboarding of insecure equipment that lacks necessary protections. As modern cities transition into hyper-connected hubs, the rapid deployment of smart utility meters, automated traffic signals, and advanced surveillance systems has prioritized immediate operational benefits over long-term digital safety. This imbalance creates a precarious environment where the very systems designed to enhance public welfare simultaneously introduce profound vulnerabilities into the municipal network. By the current cycle of 2026, the complexity of these distributed ecosystems has grown exponentially, often leaving municipal IT departments struggling to maintain a cohesive defense against sophisticated actors. The fundamental issue is not merely the presence of these devices, but the lack of a standardized governance model that integrates security into the lifecycle of every connected asset from the very moment of its conception or purchase.
Asset Management: Achieving Visibility and Procurement Control
The proliferation of “shadow IT” within local government agencies presents a significant hurdle for maintaining a secure technological perimeter. Departmental leaders in public works or emergency services frequently acquire niche IoT solutions to address specific localized challenges, such as monitoring water pressure or tracking fleet vehicles, without coordinating with centralized information technology teams. This siloed approach results in a vast array of hardware that operates outside the scope of traditional security monitoring and vulnerability management programs. Without a centralized inventory, these devices often remain in the field with factory-default credentials and outdated firmware, serving as neglected backdoors for potential intruders. The absence of visibility means that a security team cannot protect what it does not know exists, turning essential public infrastructure into unmonitored risk vectors. Addressing this requires a cultural shift toward total transparency across all agency divisions.
Establishing a rigorous and comprehensive asset discovery process serves as the foundational pillar for any successful IoT security strategy in the public sector. This initiative goes beyond simple identification; it requires a detailed cataloging of each device’s physical location, communication protocols, and functional ownership. In the landscape of 2026, many forward-thinking municipalities have implemented automated scanning tools that detect and profile new hardware as soon as it connects to the network. However, technical discovery must be paired with clear administrative accountability to be truly effective. Every identified device needs a designated owner responsible for its lifecycle, particularly regarding the timely application of security patches and firmware updates. By explicitly defining these roles, governments can ensure that no piece of equipment becomes a permanent, unpatched liability that compromises the integrity of the entire municipal digital ecosystem and citizen data over time.
Systemic Defense: Technical Containment and Governance Frameworks
Once devices are vetted and deployed, technical containment through network segmentation becomes the primary line of defense against lateral movement. In a modern government environment, IoT hardware should never be granted unfettered access to the core administrative network that houses sensitive citizen records or financial databases. Instead, these devices must be isolated within specialized virtual local area networks that employ a “least privilege” communication model. This architectural approach ensures that a smart streetlight or a traffic camera can only communicate with the specific management server it requires to function and nothing else. Should a single device be compromised, the segmentation prevents the threat from spreading across the wider infrastructure, effectively neutralizing the risk of a full-scale breach. This containment strategy is essential for protecting the essential services that residents rely on, ensuring that a localized failure does not lead to a systemic crisis.
The successful integration of these strategic measures provided a robust foundation for the continued digital evolution of municipal services. Government agencies that prioritized governance over convenience were able to neutralize the risks associated with rapid IoT adoption while maximizing the operational benefits of connected technology. By moving away from reactive responses, these organizations established a resilient infrastructure that protected both critical public assets and the private data of their constituents. The implementation of standardized procurement cycles and technical containment strategies fundamentally altered the way local governments approached technological growth, turning security into a catalyst for innovation rather than a barrier. These proactive steps ensured that the essential utilities and safety systems remained operational during periods of increased digital volatility. Ultimately, the shift toward a unified and framework-based security posture secured the long-term reliability of the modern smart city.