The automated rotation of database passwords and API keys is a cornerstone of modern cloud security, yet for many Go developers, it remains a recurring source of operational dread. While AWS Secrets Manager dutifully updates a credential every thirty days, the application consuming it often remains unaware of the change, clutching an expired token in memory until a connection failure triggers a late-night incident response. In this scenario, a security best practice becomes a catalyst for downtime, forcing teams to choose between the friction of manual pod restarts and the risk of service interruptions during critical business hours.
The persistence of these failures highlights a fundamental mismatch between security policies and application architecture. When a process fails to recognize that its underlying authentication data changed, the resulting errors often manifest as intermittent database timeouts or unauthorized API responses that are difficult to debug in real-time. This instability undermines the very trust that automated rotation is supposed to build, leading many organizations to delay security updates in favor of maintaining uptime.
The Stale Credential Trap: Why Your Service Fails After Secret Rotation
The disconnect stems from a fundamental design pattern where most Go services are built to be static, reading configuration and secrets only once during the initial startup phase. In a dynamic cloud environment where infrastructure evolves in real-time, this one-and-done approach is no longer sustainable for modern reliability standards. As organizations scale, the overhead of redeploying hundreds of microservices just to refresh a rotated secret creates significant operational friction that slows down development velocity.
Moreover, the technical debt associated with static configuration often leads to brittle deployments where a single expired credential can cascade through a distributed system. If a central database password rotates but only half of the connecting microservices successfully restart to pick up the new value, the resulting partial outage can be more damaging than a total shutdown. There is a pressing need for a reconciliation layer that allows applications to observe infrastructure changes and adapt their internal state without requiring a full process restart or manual human intervention.
Bridging the Gap: Infrastructure Automation and Runtime Awareness
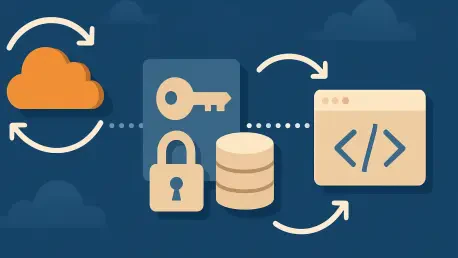
Mamori solves this rotation dilemma by acting as a live synchronization engine between AWS and the running Go application, ensuring that credentials stay current without the need for redeployment. It categorizes external data using a clear URI-based system that distinguishes between sensitive secrets and standard configuration. This approach allows developers to treat remote configuration as a living stream of data rather than a fixed snapshot taken at boot time.
The shift toward runtime awareness enables a more fluid relationship between the code and its environment. By allowing the application to self-correct when a secret changes, the development team effectively decouples the security lifecycle from the deployment lifecycle. This separation of concerns ensures that security teams can increase rotation frequency—moving from thirty days to weekly or even daily intervals—without imposing any additional burden on the engineers responsible for service stability.
Decoupling Secret Management: Mamori and URI-Based Schemes
The library utilizes a specialized aws-sm:// scheme reserved for AWS Secrets Manager, which handles high-stakes data like database credentials and third-party tokens that undergo frequent rotation. For non-sensitive values such as feature flags, log levels, or worker pool sizes, the aws-ps:// scheme connects directly to the AWS Systems Manager Parameter Store. This distinction allows for a clear hierarchy of data sensitivity and ensures that each piece of information is retrieved using the most appropriate security protocol.
By using these schemes, developers consolidate environment variables, local files, and remote AWS resources into a single, typed Go struct that serves as the source of truth for the entire application. This unified mapping simplifies the internal logic of the service, as individual functions no longer need to know where a configuration value originated. Whether a value comes from a local .env file during development or a secured AWS vault in production, the application interacts with the data through a consistent and type-safe interface.
Optimizing Performance: Reliability Through Intelligent Polling
To prevent the application from becoming a burden on the AWS API or a bottleneck for network traffic, several sophisticated optimization strategies are implemented within the library. By default, a ±20% jitter is applied to the polling frequency, effectively preventing a thundering herd effect where multiple service instances attempt to refresh secrets at the exact same millisecond. This randomized distribution of requests ensures that the AWS infrastructure remains stable even when thousands of containers are monitoring for updates simultaneously.
Furthermore, the library checks the VersionId of a secret before attempting a full re-decode of the data. If the version matches the local state, the operation terminates early, making the routine checks computationally inexpensive and reducing unnecessary data transfer. To minimize latency, multiple secret requests are batched into the fewest possible API calls. The system also validates the entire configuration struct before applying updates; if a new secret is malformed or fails a schema check, the application continues using the last valid state rather than crashing.
Securing the Runtime: Redacted Types and Resilience Logic
Security extends beyond just fetching the secret; it involves ensuring that sensitive data does not leak into logs or observability platforms during its lifecycle. The secret.String type automatically redacts itself when passed to standard logging libraries or JSON encoders, outputting [REDACTED] instead of the sensitive value. This protection is critical in 2026, where compliance standards require strict data handling to prevent accidental exposure in centralized logging systems.
Developers must explicitly call a .Reveal() method to access the plaintext, a design choice that forces intentionality and enables static analysis tools to catch accidental leaks before they reach production. Recognizing that cloud APIs can experience transient failures, the library allows for the definition of a stale threshold. This ensures the application remains operational using cached credentials during brief AWS outages, only alerting engineers if the connection issue persists beyond a safe duration.
The transition toward automated, restart-free secret rotation marked a significant milestone in operational maturity for modern Go applications. Engineering teams moved toward a standard where sensitive credentials became fluid entities rather than static constraints. This shift prompted the adoption of robust validation patterns that protected against malformed updates while maintaining peak performance. Ultimately, the industry embraced a paradigm where infrastructure and code functioned in a shared state of awareness, ensuring that security enhancements no longer compromised the stability of critical systems. Organizations successfully prioritized the implementation of version-aware detection to reduce cloud costs and improved their observability pipelines through the use of redaction types. This evolution allowed developers to focus on feature delivery while the underlying reconciliation layer handled the complexities of the modern security landscape.