OpenAI is transitioning away from periodic security assessments toward a model of continuous defense that integrates external research expertise with advanced artificial intelligence. The digital landscape in 2026 requires more than just reactive patching; it demands a proactive posture that anticipates threats before they manifest in live environments. This shift reflects a broader industry trend where the speed of software development has outpaced traditional quarterly audits. By embedding security protocols directly into the development lifecycle, the organization aims to eliminate the window of opportunity that attackers often exploit between discovery and remediation. This initiative is not merely about finding bugs but about fundamentally re-engineering the relationship between model deployment and systemic safety. As generative models become deeper components of global infrastructure, the necessity for a persistent, self-healing defensive layer has become a critical priority for maintaining public trust and operational stability.
Strategic Alliances: Scaling Through Collaborative Intelligence
A cornerstone of this strategy involves a deep integration with specialized external firms like Cathedral Systems to simulate sophisticated attack vectors. Under the leadership of CEO Gavin Kliger, these researchers are tasked with executing “red teaming” exercises that push the limits of existing guardrails. This partnership moves beyond the standard consultancy model by allowing Cathedral’s team to work synchronously with internal developers, sharing real-time data and proprietary methodologies. The goal is to move toward a continuous defense cycle where identifying a weakness and validating its repair occurs within a seamless operational loop. By pressure-testing the platform from the perspective of an advanced adversary, the team can discover edge cases that might be overlooked during standard internal reviews. This collaborative environment fosters a culture of constant scrutiny, ensuring that no architectural component remains unexamined during the ongoing security sprint.
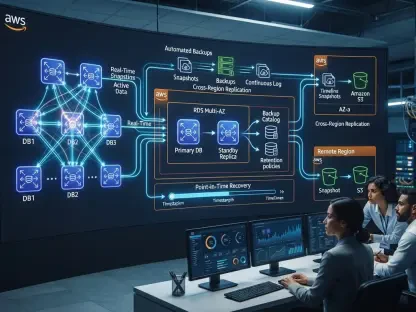
The technical backbone of this initiative is known as the Defense Factory, a sophisticated architecture designed to autonomously manage the threat landscape. This system utilizes specialized AI agents that are programmed to map out internal infrastructures and identify potential entry points for malicious actors. These agents act as persistent sentinels, scanning for anomalies and investigating potential flaws without requiring constant human intervention. One of the most critical aspects of the Defense Factory is its ability to test these vulnerabilities in strictly isolated environments. This ensures that experimental security probes do not interfere with the performance or availability of live services used by millions of people. By creating a digital twin of the infrastructure for testing purposes, the system can safely explore dangerous scenarios. This approach allows for a level of aggressive testing that was previously impossible, providing a safe sandbox for discovering how various system components might interact.
Internal Resource Allocation and Community Defense
Internally, the organization has undergone a massive structural reorganization to support this persistent defensive posture. Approximately 25% of the total product engineering workforce has been reassigned to security-centric roles, emphasizing that protection is a core feature rather than a secondary consideration. These engineers utilize specialized tools like Codex to automate the more repetitive and labor-intensive aspects of vulnerability research. For instance, AI-driven automation now handles the initial stages of reproducing reported flaws, allowing human experts to focus on the high-level logic required for complex architectural changes. To supplement this, the bug bounty program was expanded to offer rewards up to $172,000 for exceptional findings. This internal reallocation of talent ensures that security insights are integrated into the product at the code level, rather than being applied as an external patch. By leveraging AI technologies, the organization creates a feedback loop that grows more resilient as the models themselves become more capable.
The implementation of the continuous defense model established a new standard for how AI companies approached systemic risk and vulnerability management. By integrating automated discovery with human-led verification, the strategy mitigated thousands of potential threats before they reached the production stage. This commitment was further solidified by the Daybreak for Frontline Defenders initiative, a $1 billion program that provided essential services with subsidized access to advanced security tools. Organizations looking to adopt similar frameworks prioritized the creation of isolated testing environments and invested in partnerships to gain an outside-in perspective on their security. The shift toward higher bounty payouts successfully redirected talent from adversarial markets toward collaborative research, proving that financial incentives were a powerful tool. It became clear that maintaining a defensive edge required a shift in how personnel and machine intelligence interacted. Moving forward, the industry learned that the most resilient systems were those that treated security as a living process.