Because WSO2 is a foundational component for many SaaS providers, this access control flaw represents a significant risk to global digital supply chains. The discovery of CVE-2025-11969 marks a pivotal moment for enterprise security teams who rely on these gateway systems to facilitate seamless
The rapid evolution of continuous integration and continuous delivery pipelines has inadvertently created a massive surface area for sophisticated cyberattacks that target the very tools meant to automate and secure the development process. A critical remote code execution vulnerability, identified
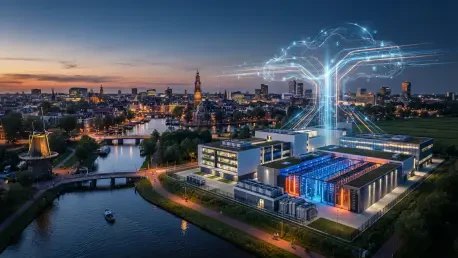
Alibaba Cloud’s President of International Business, Feifei Li, emphasized that the Dutch expansion is essential for businesses that need to scale their AI workloads securely. This strategic move marks a significant shift in the European cloud landscape as the provider opens two sophisticated data

When suspicious behavior is flagged, an investigative agent reconstructs the event from available evidence to determine if a security boundary has been violated. This principle drives a new architectural shift in how frontier models are secured against emerging threats in 2026. The transition to a

Current industry data reveals that 38% of manufacturing workers share credentials, the highest rate of any surveyed sector, to avoid the frustration of repetitive authentication. This systemic behavior arises from a fundamental conflict between necessary cybersecurity protocols and the relentless
A high-severity vulnerability in GitLab Enterprise Edition highlights the dangers of insufficient input validation when bridging user inputs with a high-privilege CI execution context. On August 26, 2026, the company issued critical patches to address a significant flaw within its Duo Claude AI
1 2 3 4 5 6 7 8 9 10 11 12 13 14 15 16 17 18 19 20 21 22 23 24 25 26 27 28 29 30 31 32 33 34 35 36 37 38 39 40 41 42 43 44 45 46 47 48 49 50 51 52 53 54 55 56 57 58 59 60 61 62 63 64 65 66 67 68 69 70 71 72 73 74 75 76 77 78 79 80 81 82 83 84 85 86 87 88 89 90 91 92 93 94 95 96 97 98 99 100