The landscape of software development shifted dramatically when a coordinated wave of automated intrusions successfully weaponized the trust inherent in open-source collaboration platforms to harvest sensitive credentials at an unprecedented scale. Known as the wfx-loot campaign, this operation
The development of vibe-qc marks a transition where individual researchers can maintain sophisticated software suites that previously demanded massive institutional resources and years of labor. This evolution, spearheaded by Dr. Michael F. Peintinger at the University of Bonn, represents a
Postmortem debugging for GPUs now utilizes a common base class for core-dump analysis across different hardware vendor implementations. This development marks a significant shift in how developers approach the debugging of complex AI and high-performance computing workloads that move seamlessly
The recent discovery of the GhostAction campaign has sent shockwaves through the global development community as security researchers revealed a massive compromise affecting over 30,000 GitHub repositories. This sophisticated supply chain attack managed to breach approximately 1,900 maintainer
Technical disagreements regarding vulnerability severity or root causes are handled transparently by recording differing assessments as attributable, structured data rather than overwriting historical records. This approach marks a significant shift in how security professionals approach the
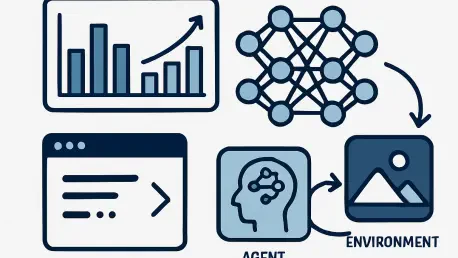
Evaluating a policy with the evaluate_policy helper provides a streamlined way to calculate the mean reward across multiple episodes without manual loop construction. This capability sits at the heart of Stable-Baselines3, a library that has fundamentally transformed how researchers and developers
1 2 3 4 5 6 7 8 9 10 11 12 13 14 15 16 17 18 19 20 21 22 23 24 25 26 27 28 29 30 31 32 33 34 35 36 37 38 39 40 41 42 43 44 45 46 47 48