Transitioning from annual audits to continuous assessment models has become a necessity as static scores fail to account for the rapid threat drift occurring between traditional audit cycles. In the current cybersecurity environment, organizations face a landscape where threats evolve weekly,
For over twenty years, software engineers have performed a digital penance, spending countless hours meticulously repairing the brittle scripts that sustain the modern internet; this labor-intensive cycle of Quality Assurance (QA) reached a critical saturation point as software complexity outpaced
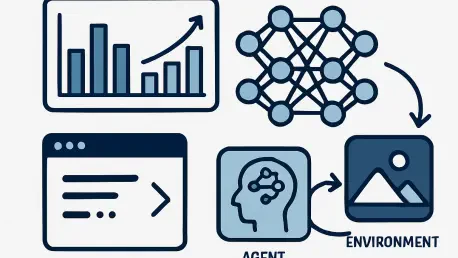
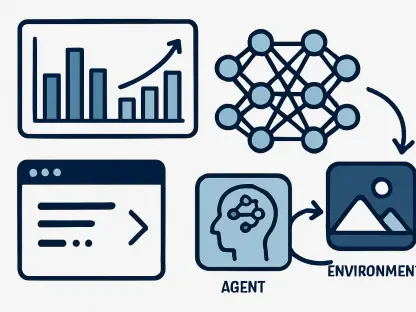
Evaluating a policy with the evaluate_policy helper provides a streamlined way to calculate the mean reward across multiple episodes without manual loop construction. This capability sits at the heart of Stable-Baselines3, a library that has fundamentally transformed how researchers and developers
The persistent struggle to synchronize disparate data systems frequently forces engineering teams to choose between the specialized power of a dedicated search engine and the intricate relationship mapping of a graph database. For years, the standard response to a full-text search requirement has
Operating as a modular penetration-testing suite, ARTEX utilizes a tiered agent system where a planner decomposes high-level goals into actionable tasks for worker sub-agents. This sophisticated framework integrates a Go-based backend with a highly responsive Next.js front-end console, allowing for
A comprehensive passkey strategy involves monitoring credential usage through lifecycle callbacks, providing users with visibility into when each of their security keys was last accessed. This necessity stems from the evolving landscape of digital security, where simply offering a passkey
1 2 3 4 5 6 7 8 9 10 11 12 13 14 15 16 17 18 19 20 21 22 23 24 25 26 27 28 29 30 31 32 33 34 35 36 37 38 39 40 41 42 43