Modern enterprise security depends heavily on the integrity of the software supply chain, as evidenced by the numerous library-based vulnerabilities patched this month. The recent security bulletin released by Atlassian for November 2026 marks a high point in the company's efforts to secure its
The sudden collapse of perimeter-based security is often punctuated by high-profile incidents that demonstrate how a single oversight in a third-party supply chain can jeopardize an entire corporate infrastructure. This reality was made clear during a concentrated 44-hour breach between November 1
The sheer velocity at which modern large language models can generate executable code has fundamentally altered the rhythm of software development cycles, yet this rapid output often conceals a growing burden of structural decay. This transition from a human-centric approach to AI-assisted delivery
Modern security workflows now prioritize routing vulnerability findings directly to developers as pull requests rather than sending them to a generic security inbox. This fundamental shift marks a departure from the reactive models of the past decade, placing the responsibility and the capability
The integration of AI agents into production-grade software necessitates robust verification tools to prevent the introduction of new security vulnerabilities or logic flaws. As the software engineering landscape evolves, Google has officially expanded its generative ecosystem with the introduction
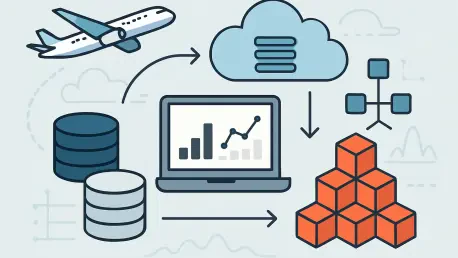
Aerospace organizations frequently struggle to unlock sensor-derived telemetry that remains trapped within specialized proprietary formats incompatible with standard analytics engines. This technical isolation often hinders critical safety analysis and operational improvements, as the data remains
1 2 3 4 5 6 7 8 9 10 11 12 13 14 15 16 17 18 19 20 21 22 23 24 25 26 27 28 29 30 31 32 33 34 35 36 37 38 39 40 41 42 43 44 45 46 47 48 49 50 51 52 53 54 55 56 57 58 59 60 61 62 63 64 65 66 67 68 69 70 71 72 73 74 75 76 77 78 79 80