Enterprise customers are increasingly leveraging their financial commitments to AI providers to purchase third-party software and services directly within integrated marketplaces. This fundamental transformation suggests that artificial intelligence is rapidly outgrowing its initial role as a
Legacy development roles must evolve into verification specialists and context curators to handle the multi-threaded nature of asynchronous AI coding. In the current landscape of 2026, the traditional software development lifecycle is no longer a human-powered engine supported by tools, but rather
The Private Computing Cloud now includes a Transparency Report log that allows individuals to track exactly when and how their personal data was processed by AI services. This milestone in user privacy arrives alongside the official debut of ColorOS 17, representing a fundamental shift in the
On-device Neural Processing Units allow employees to handle AI workloads locally so that sensitive corporate data never leaves the laptop's physical boundary. This technological advancement serves as a critical cornerstone in a professional landscape where the traditional office perimeter has
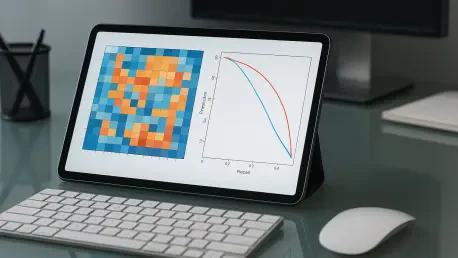
Establishing a non-machine learning baseline is a vital step in preventing over-engineered solutions that offer only marginal improvements over simple rules. The pressure to build autonomous systems is real, and it has pushed traditional IT operations to their limits. Many organizations now pursue
Modern engineering leaders are moving away from security as a pipeline blocker and instead integrating it as an invisible enabler that rides alongside code from inception to production. This transformation has redefined the relationship between developers and security teams, creating a unified
A single lambda:InvokeFunction permission was sufficient for an attacker to ride a privileged execution role past strictly defined account-level restrictions. This sophisticated privilege-escalation vulnerability, identified as CVE-2026-94384, was quietly addressed by AWS in the summer of 2026
The FBI disruption of the QakBot infrastructure in 2023 revealed a massive network consisting of more than 700,000 infected computers worldwide. This staggering figure highlights the immense scale at which modern botnet groups operate, transforming thousands of individual devices into a unified,
Security analysts have identified a crisis of default-open internal architectures where the integrity of a private network is wrongly substituted for robust design. This systemic failure to implement fundamental authentication protocols within critical infrastructure control planes has become a
The discovery of a missing authorization check on the /config/update endpoint reveals how low-privileged accounts can bypass security protocols to modify a gateway's runtime configuration. This architectural flaw, identified in the LiteLLM gateway version 1.77.7, fundamentally undermines the
1 2 3 4 5 6 7 8 9 10 11 12 13 14 15 16 17 18 19 20 21 22 23 24 25 26 27 28 29 30 31 32 33 34 35 36 37 38 39 40 41 42 43 44 45 46 47 48 49 50 51 52 53 54 55 56 57 58 59 60 61 62 63 64 65 66 67 68 69 70 71 72 73 74 75 76 77 78 79 80 81 82 83 84 85 86 87 88 89 90


